Buy casinojobs.eu ?
We are moving the project
casinojobs.eu .
Are you interested in purchasing the domain
casinojobs.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy casinojobs.eu ?
What is the TPM 2 bug in Valorant?
The TPM 2 bug in Valorant refers to a compatibility issue with the Trusted Platform Module (TPM) 2.0 security feature on certain computers. This bug prevents players from launching the game and results in an error message stating that the system does not meet the minimum requirements. Riot Games, the developer of Valorant, has acknowledged the issue and is working on a fix to address the problem. In the meantime, affected players may need to disable the TPM 2.0 feature in their computer's BIOS settings in order to play the game. **
How can I activate TPM on Windows 2?
To activate TPM on Windows 2, you can follow these steps: 1. First, access the BIOS or UEFI settings of your computer by restarting it and pressing the appropriate key (often F2, F10, or Del) during the boot process. 2. Once in the BIOS or UEFI settings, look for the Security or TPM section and enable TPM. The exact location and wording may vary depending on your computer's manufacturer. 3. Save the changes and exit the BIOS or UEFI settings. Your computer will restart, and TPM should now be activated on Windows 2. It's important to note that not all computers support TPM, so you may need to check your computer's specifications to ensure it has TPM capabilities. **
Similar search terms for TPM-2-0-Encryption
Top-Angebote
Products related to TPM-2-0-Encryption:
-
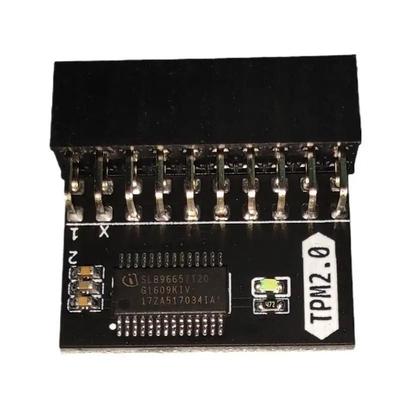
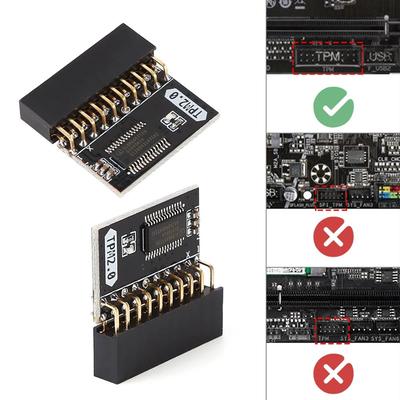
TPM 2.0 20 Pin Encryption Security Module | LPC Hardware Based Encryption For ASUS, MSI, ASROCK, & GIGABYTE TPM 2.0 20 Pin Encryption Security Module | LPC Hardware Based Encryption For ASUS, MSI, ASROCK, & GIGABYTEInaugurate a powerful SecuritySanctuary energy for your computational core with the ultimate 2026 hardware encryption solution. The TPM 2.0 20Pin Security Module is the premier choice for creating a TechnicalModern or StudioLuxe atmosphere for your...74,97 $*Shipping: 0,00 $Secure redirect to the provider
-
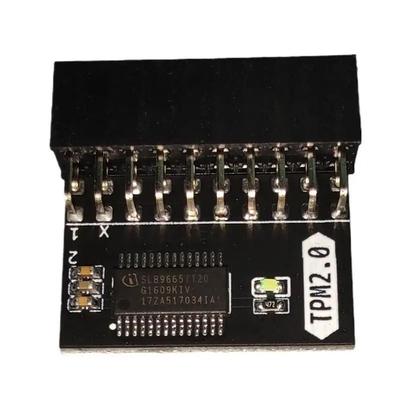
TPM 2.0 20 Pin Encryption Security Module For Motherboards greenEnhance your system security and compatibility with this reliable TPM 2.0 module designed for supported ASUS, MSI, ASRock, and Gigabyte motherboards. Built to provide hardwarelevel encryption support, this security module helps protect sensitive...100,45 $*Shipping: 0,00 $Secure redirect to the provider
-
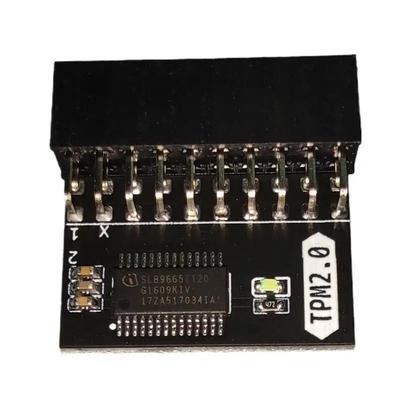
TPM 2.0 Security Module Board For ASUS & Gigabyte Motherboards LPC 20 Pin Hardware Encryption For Windows 11 TPM 2.0 Security Module Board For ASUS & Gigabyte Motherboards LPC 20 Pin Hardware Encryption For Windows 11Upgrade your PCs security and unlock full Windows 11 compatibility with a reliable, plugandplay TPM 2.0 module built for modern motherboards. Designed for users who value data protection and system stability, this compact board delivers...74,97 $*Shipping: 0,00 $Secure redirect to the provider
-
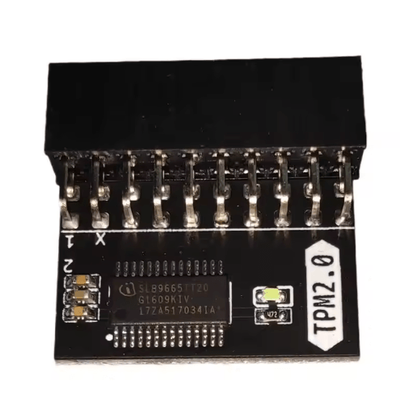
TPM 2.0 20 Pin Security Module LPC Encryption Board For ASUS MSI ASRock Gigabyte greenUpgrade your PCs security without replacing your entire system. This TPM 2.0 module is designed for users who need enhanced data protection, secure boot, and modern system compatibility. By adding a dedicated hardware chip, this TPM 2.0 security...85,00 $*Shipping: 0,00 $Secure redirect to the provider

-
I have a few questions about TPM security.
Sure, I'd be happy to help with your questions about TPM security. Please go ahead and ask your questions, and I'll do my best to provide you with accurate and helpful information. **
-
Does the B450 Gaming Plus Max have TPM?
The B450 Gaming Plus Max does not have a built-in TPM (Trusted Platform Module) chip. However, you can add a TPM module to the motherboard if you need to use TPM for security features such as BitLocker encryption. Keep in mind that not all motherboards come with a TPM header, so you may need to check the specifications of the B450 Gaming Plus Max to ensure compatibility with a TPM module. **
-
"Does my Asus B450-F Gaming support TPM 2.0?"
Yes, the Asus B450-F Gaming motherboard does support TPM 2.0. This motherboard has a TPM header, which allows you to connect a TPM module to enable TPM functionality. TPM (Trusted Platform Module) is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption and secure boot. By adding a TPM module to the motherboard, you can enhance the security of your system and protect sensitive data. **
-
What are the digits 0 and 2?
The digit 0 is the numerical representation of the absence of quantity or value. It is often used as a placeholder in the decimal system. The digit 2 is a numerical symbol representing the quantity or value of two. It is used in various mathematical operations and calculations. **


Why is 0^2 equal to 001?
The expression 0^2 is equal to 0 multiplied by 0, which equals 0. When written in a three-digit format, 0 is represented as 000. Therefore, 0^2 can be written as 000^2, which equals 000. This can also be represented as 001 in a three-digit format. Therefore, 0^2 is equal to 001. **
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Top-Angebote
Products related to TPM-2-0-Encryption:
-
TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade Card TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade CardProtect your digital life and unlock the full potential of your PC with the TPM 2.0 Encryption Security Module. As security requirements for modern operating systems become more stringent, this 20pin TPM module serves as the essential hardwarebased...80,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PC TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PCProtect your system with enhanced security using this TPM 2.0 module designed for reliable data encryption and system integrity. Ideal for users upgrading their PC security, this module works seamlessly with supported motherboards to enable advanced...57,98 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 20 Pin Encryption Security Module | LPC Hardware Based Encryption For ASUS, MSI, ASROCK, & GIGABYTE TPM 2.0 20 Pin Encryption Security Module | LPC Hardware Based Encryption For ASUS, MSI, ASROCK, & GIGABYTEInaugurate a powerful SecuritySanctuary energy for your computational core with the ultimate 2026 hardware encryption solution. The TPM 2.0 20Pin Security Module is the premier choice for creating a TechnicalModern or StudioLuxe atmosphere for your...74,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 20 Pin Encryption Security Module For Motherboards greenEnhance your system security and compatibility with this reliable TPM 2.0 module designed for supported ASUS, MSI, ASRock, and Gigabyte motherboards. Built to provide hardwarelevel encryption support, this security module helps protect sensitive...100,45 $*Shipping: 0,00 $Secure redirect to the provider
-
What is the TPM 2 bug in Valorant?
The TPM 2 bug in Valorant refers to a compatibility issue with the Trusted Platform Module (TPM) 2.0 security feature on certain computers. This bug prevents players from launching the game and results in an error message stating that the system does not meet the minimum requirements. Riot Games, the developer of Valorant, has acknowledged the issue and is working on a fix to address the problem. In the meantime, affected players may need to disable the TPM 2.0 feature in their computer's BIOS settings in order to play the game. **
-
How can I activate TPM on Windows 2?
To activate TPM on Windows 2, you can follow these steps: 1. First, access the BIOS or UEFI settings of your computer by restarting it and pressing the appropriate key (often F2, F10, or Del) during the boot process. 2. Once in the BIOS or UEFI settings, look for the Security or TPM section and enable TPM. The exact location and wording may vary depending on your computer's manufacturer. 3. Save the changes and exit the BIOS or UEFI settings. Your computer will restart, and TPM should now be activated on Windows 2. It's important to note that not all computers support TPM, so you may need to check your computer's specifications to ensure it has TPM capabilities. **
-
I have a few questions about TPM security.
Sure, I'd be happy to help with your questions about TPM security. Please go ahead and ask your questions, and I'll do my best to provide you with accurate and helpful information. **
-
Does the B450 Gaming Plus Max have TPM?
The B450 Gaming Plus Max does not have a built-in TPM (Trusted Platform Module) chip. However, you can add a TPM module to the motherboard if you need to use TPM for security features such as BitLocker encryption. Keep in mind that not all motherboards come with a TPM header, so you may need to check the specifications of the B450 Gaming Plus Max to ensure compatibility with a TPM module. **
Similar search terms for TPM-2-0-Encryption
-
TPM 2.0 Security Module Board For ASUS & Gigabyte Motherboards LPC 20 Pin Hardware Encryption For Windows 11 TPM 2.0 Security Module Board For ASUS & Gigabyte Motherboards LPC 20 Pin Hardware Encryption For Windows 11Upgrade your PCs security and unlock full Windows 11 compatibility with a reliable, plugandplay TPM 2.0 module built for modern motherboards. Designed for users who value data protection and system stability, this compact board delivers...74,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 20 Pin Security Module LPC Encryption Board For ASUS MSI ASRock Gigabyte greenUpgrade your PCs security without replacing your entire system. This TPM 2.0 module is designed for users who need enhanced data protection, secure boot, and modern system compatibility. By adding a dedicated hardware chip, this TPM 2.0 security...85,00 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Security Module Board For ASUS MSI GIGABYTE ASRock 12 14 18 20 Pin Remote Encryption Module aEnhance your PCs security with the TPM 2.0 Security Module Board, built to protect data and enable trusted hardwarelevel encryption. Compatible with major motherboard brands including ASUS, MSI, GIGABYTE, and ASRock, this module supports multiple...44,95 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Security Module Board For ASUS MSI GIGABYTE ASRock 12 14 18 20 Pin Remote Encryption Module gEnhance your PCs security with the TPM 2.0 Security Module Board, built to protect data and enable trusted hardwarelevel encryption. Compatible with major motherboard brands including ASUS, MSI, GIGABYTE, and ASRock, this module supports multiple...44,95 $*Shipping: 0,00 $Secure redirect to the provider
-
"Does my Asus B450-F Gaming support TPM 2.0?"
Yes, the Asus B450-F Gaming motherboard does support TPM 2.0. This motherboard has a TPM header, which allows you to connect a TPM module to enable TPM functionality. TPM (Trusted Platform Module) is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption and secure boot. By adding a TPM module to the motherboard, you can enhance the security of your system and protect sensitive data. **
-
What are the digits 0 and 2?
The digit 0 is the numerical representation of the absence of quantity or value. It is often used as a placeholder in the decimal system. The digit 2 is a numerical symbol representing the quantity or value of two. It is used in various mathematical operations and calculations. **
-
Why is 0^2 equal to 001?
The expression 0^2 is equal to 0 multiplied by 0, which equals 0. When written in a three-digit format, 0 is represented as 000. Therefore, 0^2 can be written as 000^2, which equals 000. This can also be represented as 001 in a three-digit format. Therefore, 0^2 is equal to 001. **
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.