Buy casinojobs.eu ?
We are moving the project
casinojobs.eu .
Are you interested in purchasing the domain
casinojobs.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy casinojobs.eu ?
How is the Asus TPM module used?
The Asus TPM module is used to enhance the security of a computer system by providing hardware-based encryption capabilities. It helps to protect sensitive data such as passwords, encryption keys, and digital certificates. The TPM module works by securely storing and managing these cryptographic keys, ensuring that they cannot be easily accessed or tampered with by unauthorized users. Overall, the Asus TPM module helps to strengthen the overall security posture of a computer system. **
Which motherboards support the TPM 2.0 module?
Motherboards that support the TPM 2.0 module typically include high-end models designed for business or security-focused applications. Some examples of motherboard manufacturers known to support TPM 2.0 modules include ASUS, Gigabyte, MSI, and ASRock. It's important to check the specifications of the specific motherboard model you are interested in to ensure it has the necessary TPM header or slot for the module. **


Similar search terms for TPM-2-0-Module
Top-Angebote
Products related to TPM-2-0-Module:
-
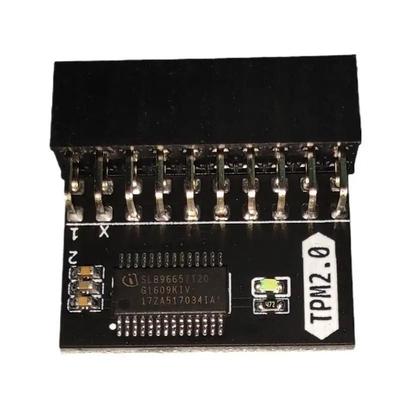
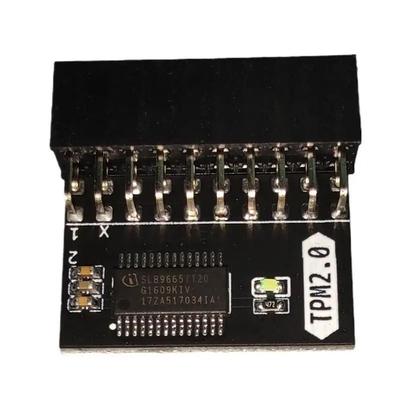
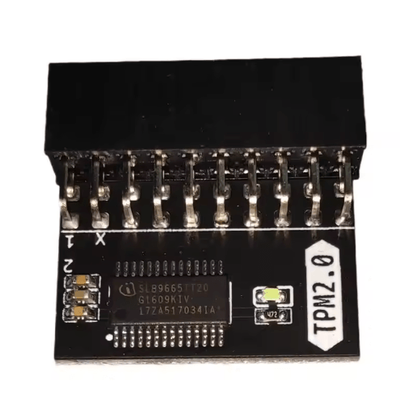
TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade Card TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade CardProtect your digital life and unlock the full potential of your PC with the TPM 2.0 Encryption Security Module. As security requirements for modern operating systems become more stringent, this 20pin TPM module serves as the essential hardwarebased...80,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PC TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PCProtect your system with enhanced security using this TPM 2.0 module designed for reliable data encryption and system integrity. Ideal for users upgrading their PC security, this module works seamlessly with supported motherboards to enable advanced...57,98 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 20 Security Module Board For PC Motherboards greenProtect your system and upgrade your computer security with this TPM 20 module designed for compatible desktop motherboards. Built for users who want stronger data protection and reliable system authentication this security module helps support...57,48 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Module 20 Pin Motherboard Security Chip For ASUS MSI Gigabyte TPM 2.0 Module 20 Pin Motherboard Security Chip For ASUS MSI GigabyteProtect your data and unlock advanced system security with this reliable TPM 2.0 module designed for modern motherboards. Built for users who value privacy, secure boot, and Windows 11 compatibility, this compact upgrade enhances your PCs defense...62,97 $*Shipping: 0,00 $Secure redirect to the provider


-
What is the update for the TPM 2.0 module?
The update for the TPM 2.0 module includes enhancements to security features, bug fixes for known vulnerabilities, and improved compatibility with the latest hardware and software. It may also include performance optimizations and updates to cryptographic algorithms to ensure the module remains secure and reliable. Users are encouraged to regularly check for updates to keep their TPM 2.0 module up to date with the latest improvements and security patches. **
-
What is the TPM module of the ASUS ROG Strix X570-E Gaming?
The TPM (Trusted Platform Module) module of the ASUS ROG Strix X570-E Gaming is a hardware-based security feature that provides a secure foundation for the system. It is a dedicated microcontroller that stores cryptographic keys, passwords, and other sensitive data securely. The TPM module helps to protect against unauthorized access to the system and ensures the integrity of the system's boot process and sensitive data. It is an essential component for ensuring the security of the system and protecting against various types of attacks. **
-
Can the true identity be determined using the TPM module?
The TPM (Trusted Platform Module) module is designed to securely store and protect cryptographic keys, which can be used to verify the integrity of a system and its components. While the TPM can provide a level of assurance about the authenticity of a system, it is not designed to determine the true identity of an individual. The TPM can be used to verify the integrity of a system and its components, but it cannot directly determine the true identity of the user or owner of the system. Determining true identity typically involves a combination of factors such as biometric authentication, multi-factor authentication, and identity verification processes. **
-
Is the Asus TPM 2.0 module not recognized in the BIOS?
If the Asus TPM 2.0 module is not recognized in the BIOS, it could be due to several reasons. First, ensure that the module is properly installed in the motherboard and that it is compatible with the BIOS version. Additionally, check if the TPM module is enabled in the BIOS settings. If it is still not recognized, it could be a compatibility issue or a faulty TPM module. In such cases, contacting Asus support or referring to the motherboard's manual for troubleshooting steps would be advisable. **

What would happen if the TPM module for PCs did not exist?
If the TPM module for PCs did not exist, it would leave computers and their data more vulnerable to security threats. The TPM module provides a secure area within the computer for storing sensitive information such as encryption keys, digital certificates, and passwords. Without this module, it would be easier for hackers to access and compromise this information, leading to potential data breaches and privacy violations. Additionally, the absence of TPM could make it more challenging to implement secure boot processes and encryption, further exposing PCs to security risks. **
After resetting the laptop, what happens to the Trusted Platform Module (TPM)?
After resetting the laptop, the Trusted Platform Module (TPM) will be reset to its default state. This means that any data stored in the TPM, such as encryption keys and credentials, will be erased. The TPM will need to be reconfigured and set up again with new keys and credentials to enable secure boot and encryption features. **
Top-Angebote
Products related to TPM-2-0-Module:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
TPM 2.0 20 Pin Security Module Board TPM 2.0 20 Pin Security Module BoardProduct Description: Upgrade your system security with this TPM 2.0 encryption module designed for compatible motherboards. It provides hardwarelevel protection for sensitive data, enabling secure boot, encryption, and full support for modern...71,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade Card TPM 2.0 Encryption Security Module 20 Pin Motherboard Upgrade CardProtect your digital life and unlock the full potential of your PC with the TPM 2.0 Encryption Security Module. As security requirements for modern operating systems become more stringent, this 20pin TPM module serves as the essential hardwarebased...80,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PC TPM 2.0 Module 20 Pin Motherboard Security Encryption Board For PCProtect your system with enhanced security using this TPM 2.0 module designed for reliable data encryption and system integrity. Ideal for users upgrading their PC security, this module works seamlessly with supported motherboards to enable advanced...57,98 $*Shipping: 0,00 $Secure redirect to the provider
-
How is the Asus TPM module used?
The Asus TPM module is used to enhance the security of a computer system by providing hardware-based encryption capabilities. It helps to protect sensitive data such as passwords, encryption keys, and digital certificates. The TPM module works by securely storing and managing these cryptographic keys, ensuring that they cannot be easily accessed or tampered with by unauthorized users. Overall, the Asus TPM module helps to strengthen the overall security posture of a computer system. **
-
Which motherboards support the TPM 2.0 module?
Motherboards that support the TPM 2.0 module typically include high-end models designed for business or security-focused applications. Some examples of motherboard manufacturers known to support TPM 2.0 modules include ASUS, Gigabyte, MSI, and ASRock. It's important to check the specifications of the specific motherboard model you are interested in to ensure it has the necessary TPM header or slot for the module. **
-
What is the update for the TPM 2.0 module?
The update for the TPM 2.0 module includes enhancements to security features, bug fixes for known vulnerabilities, and improved compatibility with the latest hardware and software. It may also include performance optimizations and updates to cryptographic algorithms to ensure the module remains secure and reliable. Users are encouraged to regularly check for updates to keep their TPM 2.0 module up to date with the latest improvements and security patches. **
-
What is the TPM module of the ASUS ROG Strix X570-E Gaming?
The TPM (Trusted Platform Module) module of the ASUS ROG Strix X570-E Gaming is a hardware-based security feature that provides a secure foundation for the system. It is a dedicated microcontroller that stores cryptographic keys, passwords, and other sensitive data securely. The TPM module helps to protect against unauthorized access to the system and ensures the integrity of the system's boot process and sensitive data. It is an essential component for ensuring the security of the system and protecting against various types of attacks. **
Similar search terms for TPM-2-0-Module
-
TPM 20 Security Module Board For PC Motherboards greenProtect your system and upgrade your computer security with this TPM 20 module designed for compatible desktop motherboards. Built for users who want stronger data protection and reliable system authentication this security module helps support...57,48 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 Module 20 Pin Motherboard Security Chip For ASUS MSI Gigabyte TPM 2.0 Module 20 Pin Motherboard Security Chip For ASUS MSI GigabyteProtect your data and unlock advanced system security with this reliable TPM 2.0 module designed for modern motherboards. Built for users who value privacy, secure boot, and Windows 11 compatibility, this compact upgrade enhances your PCs defense...62,97 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 20 Pin Security Module For Motherboards (ASUS MSI ASRock Gigabyte) TPM 2.0 20 Pin Security Module For Motherboards (ASUS MSI ASRock Gigabyte)Strengthen your PCs security with a TPM 2.0 module designed to protect sensitive data at the hardware level. This compact addon installs directly onto your motherboard, enabling secure encryption for passwords, keys, and system integrity checks....67,99 $*Shipping: 0,00 $Secure redirect to the provider
-
TPM 2.0 20 Pin Encryption Security Module For Motherboards greenEnhance your system security and compatibility with this reliable TPM 2.0 module designed for supported ASUS, MSI, ASRock, and Gigabyte motherboards. Built to provide hardwarelevel encryption support, this security module helps protect sensitive...100,45 $*Shipping: 0,00 $Secure redirect to the provider
-
Can the true identity be determined using the TPM module?
The TPM (Trusted Platform Module) module is designed to securely store and protect cryptographic keys, which can be used to verify the integrity of a system and its components. While the TPM can provide a level of assurance about the authenticity of a system, it is not designed to determine the true identity of an individual. The TPM can be used to verify the integrity of a system and its components, but it cannot directly determine the true identity of the user or owner of the system. Determining true identity typically involves a combination of factors such as biometric authentication, multi-factor authentication, and identity verification processes. **
-
Is the Asus TPM 2.0 module not recognized in the BIOS?
If the Asus TPM 2.0 module is not recognized in the BIOS, it could be due to several reasons. First, ensure that the module is properly installed in the motherboard and that it is compatible with the BIOS version. Additionally, check if the TPM module is enabled in the BIOS settings. If it is still not recognized, it could be a compatibility issue or a faulty TPM module. In such cases, contacting Asus support or referring to the motherboard's manual for troubleshooting steps would be advisable. **
-
What would happen if the TPM module for PCs did not exist?
If the TPM module for PCs did not exist, it would leave computers and their data more vulnerable to security threats. The TPM module provides a secure area within the computer for storing sensitive information such as encryption keys, digital certificates, and passwords. Without this module, it would be easier for hackers to access and compromise this information, leading to potential data breaches and privacy violations. Additionally, the absence of TPM could make it more challenging to implement secure boot processes and encryption, further exposing PCs to security risks. **
-
After resetting the laptop, what happens to the Trusted Platform Module (TPM)?
After resetting the laptop, the Trusted Platform Module (TPM) will be reset to its default state. This means that any data stored in the TPM, such as encryption keys and credentials, will be erased. The TPM will need to be reconfigured and set up again with new keys and credentials to enable secure boot and encryption features. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.